
Key Takeaways
What you need to know
Considering vCISO Services?
Get a personalized engagement recommendation
vCISO & Governance
Virtual CISO services, governance frameworks, risk assessments, and insurance-aligned cybersecurity leadership for growing organizations.
Key Capabilities
What Is a Virtual CISO?
A Virtual CISO (vCISO) is an experienced cybersecurity executive who provides strategic security leadership on a fractional basis. Unlike hiring a full-time Chief Information Security Officer—which can cost $200,000 to $400,000+ annually—a vCISO delivers the same executive-level guidance at a fraction of the cost.
This model makes enterprise-grade security leadership accessible to organizations that need strategic direction but cannot justify a full-time executive hire. Your vCISO becomes an extension of your leadership team, attending board meetings, developing security strategy, and ensuring your organization maintains a defensible security posture.
A full-time CISO costs $250,000+ annually—vCISO services deliver equivalent expertise at a fraction of the cost
Is a vCISO Right for Your Organization?
Organizations that benefit most from vCISO engagement share common characteristics. Before exploring our services, consider whether your organization aligns with the profile of companies we serve most effectively.
You're Ready for a vCISO If:
Your organization has 20-250 employees and handles sensitive client or patient data. You face regulatory requirements—FTC Safeguards, HIPAA, SOC 2, PCI, or state privacy laws—without dedicated security leadership to navigate them. Your board, investors, or strategic partners are asking security governance questions you can't confidently answer. You need to demonstrate security maturity to win contracts, close partnerships, or satisfy due diligence requirements. Cyber insurance renewals are requiring improved controls documentation, and you're unsure how to respond to carrier questionnaires.
A vCISO May Not Be the Right Fit If:
You're looking for a one-time penetration test or vulnerability scan without ongoing governance. Your organization has fewer than 20 employees with minimal regulatory exposure. You need hands-on daily IT support rather than strategic security leadership—that's a managed services engagement, not vCISO advisory. You're seeking the lowest-cost option rather than experienced counsel—we focus on organizations ready to invest in security as a business priority.
The Middle Ground
Many organizations fall somewhere between these profiles. If you're unsure whether vCISO services match your needs, our Cyber Risk Assessment provides a structured starting point. This paid engagement evaluates your current security posture and delivers actionable recommendations—whether that leads to vCISO advisory, managed services, or simply a clearer understanding of your risk landscape.
vCISO for Healthcare Organizations
Healthcare organizations face unique cybersecurity challenges that require specialized vCISO expertise. Beyond baseline compliance requirements, healthcare companies must demonstrate security maturity to partners, payers, and enterprise customers who conduct rigorous assessments before engagement.
Regulatory Complexity Beyond HIPAA
Healthcare security extends far beyond HIPAA basics. Organizations building healthcare platforms, digital health solutions, or clinical services must navigate overlapping requirements: HIPAA Security and Privacy Rules, state health information laws, FDA cybersecurity guidance for connected devices, and increasingly, SOC 2 requirements demanded by enterprise partners. A vCISO helps you understand which regulations apply to your specific business model and build a unified compliance strategy rather than treating each requirement as a separate checkbox exercise.
Partnership and Payer Requirements
Strategic healthcare partnerships increasingly require documented security programs before contracts are signed. Hospital systems, insurance payers, and enterprise healthcare buyers conduct vendor security assessments that can delay or derail partnerships if your organization lacks governance documentation. A vCISO prepares you for these assessments by building the policies, procedures, and evidence packages that due diligence teams expect to see—positioning your organization to close partnerships that competitors without security programs cannot pursue.
Building Security Into Growth
For healthcare organizations in early or growth stages, establishing security governance before operational scale prevents costly remediation later. Retrofitting compliance into an existing infrastructure is significantly more expensive and disruptive than building it correctly from the start. Our vCISO engagements scale from foundational program development through operational maturity, ensuring your security posture grows alongside your business.
Healthcare-Specific Expertise
Our team understands healthcare workflows, clinical data sensitivity, and the balance between security controls and operational efficiency that healthcare environments demand. We've guided healthcare organizations through partner security assessments, helped digital health companies establish compliance foundations, and supported practices navigating the intersection of HIPAA and emerging state privacy requirements.
When Do Organizations Need vCISO Services?
Organizations typically engage a vCISO when facing one or more of these situations:
Regulatory requirements demand documented security leadership. Whether it's FTC Safeguards Rule compliance, HIPAA security oversight, or SOC 2 preparation, regulators expect to see someone accountable for security at the executive level.
Board members or clients are asking security questions that IT cannot answer. Technical staff excel at implementation, but boards need risk-based business language and strategic recommendations.
Cyber insurance renewals have become difficult. Insurers increasingly require evidence of security governance, incident response plans, and executive oversight before offering favorable terms.
A security incident exposed gaps in your program. After a breach or near-miss, organizations often realize they need strategic leadership to prevent recurrence—not just technical fixes.
83% of organizations that experienced a breach lacked dedicated security leadership at the executive level
Our vCISO Methodology
Our vCISO engagements follow a structured methodology developed over 25 years of security leadership experience. This approach ensures consistent outcomes while adapting to each organization's unique regulatory environment, risk profile, and business objectives.
Phase 1: Security Program Assessment
Every engagement begins with a comprehensive assessment of your current security posture. This isn't a checklist audit—it's a strategic evaluation that examines your existing controls, identifies gaps against applicable regulatory frameworks, and maps findings to your specific business risks. We interview stakeholders across leadership and operations, review documentation and technical configurations, and benchmark your program against industry standards and peer organizations.
Deliverables: Risk assessment report, gap analysis mapped to compliance requirements, prioritized remediation roadmap with effort and impact estimates.
Timeline: 30-60 days depending on organizational complexity.
Phase 2: Governance Framework Development
With assessment insights established, we develop the policies, procedures, and controls framework appropriate for your organization. We focus on practical, implementable governance—documentation that reflects how your organization actually operates, not theoretical frameworks that sit unused. This phase establishes the foundation for ongoing compliance and positions you to respond confidently to partner assessments, insurance questionnaires, and regulatory inquiries.
Deliverables: Security policies tailored to your environment, incident response plan, vendor risk management framework, employee security awareness program design.
Timeline: 60-90 days, often overlapping with Phase 1 remediation priorities.
Phase 3: Ongoing Strategic Leadership
Unlike consultants who deliver a report and move on, our vCISO engagement provides continuous strategic oversight. This includes regular security briefings for leadership, compliance monitoring as regulations evolve, vendor security reviews, guidance on security investments, and representation during partner or customer security assessments. We become an extension of your leadership team, available when security questions arise and proactive about emerging risks.
Deliverables: Monthly or quarterly security briefings, compliance status tracking, board-ready reporting, strategic recommendations aligned to business priorities.
Timeline: Ongoing engagement scaled to your organization's needs.
Security programs aligned with business objectives see 3x higher adoption and sustained improvement
Why Organizations Choose CSC
Regulatory Depth, Not Just Security Breadth
We specialize in the regulatory nuances that matter to mid-sized organizations in regulated industries.
For CPA firms and financial services, we help you navigate FTC Safeguards Rule requirements that many growing firms find complex, including threshold determinations, qualified individual designations, and the specific controls regulators expect. For healthcare organizations pursuing enterprise partnerships, we help you meet the security requirements those partners expect before signing contracts, not just baseline HIPAA compliance. For organizations navigating cyber insurance, we help you demonstrate the controls that satisfy carrier questionnaires, support favorable renewal terms, and reduce coverage gaps.
This regulatory depth comes from focusing on organizations where compliance isn't optional—it's a business requirement.
National Reach, Local Understanding
Based in Las Vegas, we work with organizations nationwide through virtual engagement and on-site availability when it adds value. Our vCISO practice is built for healthcare organizations establishing their first security programs through established CPA firms strengthening governance for partner assessments.
Remote engagement works effectively for strategic advisory—we've built our practice around virtual collaboration long before it became standard. When on-site presence matters, we're available for board presentations, partner meetings, or intensive working sessions.
Principal-Led Engagement
When you engage CSC for vCISO services, you work directly with Dan Pitre—25+ years of security leadership experience, including global organizations. You receive senior-level strategic guidance from day one, not junior consultants learning on your account.
This principal-led model means faster decisions, consistent advice, and a trusted relationship with someone who understands your organization's history and objectives. Your vCISO knows your environment, your risks, and your business goals—not just your ticket queue.
vCISO Services for CPA Firms
CPA firms face unique cybersecurity challenges that make vCISO services particularly valuable. The FTC Safeguards Rule requires financial institutions—including many accounting firms—to designate a qualified individual responsible for information security.
For firms handling client financial data, tax records, and sensitive business information, the stakes are high. A data breach doesn't just trigger regulatory penalties; it destroys the trust that took decades to build.
Our vCISO services for CPA firms include Written Information Security Policy (WISP) development, FTC Safeguards compliance documentation, client data protection protocols, and the security leadership that regulations demand. We understand the accounting profession's specific requirements and speak your language.
Not sure where your firm stands on FTC Safeguards compliance? Use our free interactive FTC Safeguards Compliance Checklist to assess your information security program against all 9 required elements. You'll receive a personalized gap analysis identifying exactly where your firm needs attention—and how a vCISO engagement can help you achieve full compliance.
FTC Safeguards Rule requires a 'qualified individual' to oversee your security program—our vCISO fulfills this requirement
Assess Your FTC Safeguards Compliance
Use our free interactive checklist to evaluate your firm's information security program against all 9 FTC Safeguards Rule requirements. Get personalized gap analysis and recommendations in minutes.
What to Expect from Your vCISO Engagement
A successful vCISO relationship delivers tangible outcomes you can measure and demonstrate to stakeholders:
Documented Policies: Comprehensive security policies that satisfy regulators, insurers, and clients. No more scrambling when auditors ask for documentation.
Board-Ready Reporting: Quarterly security briefings in business language that executives understand. We translate technical risks into business impact.
Incident Response Readiness: Tested plans and procedures so your team knows exactly what to do when—not if—a security incident occurs.
Vendor Risk Management: Structured evaluation of third-party risks, ensuring your vendors don't become your vulnerability.
Continuous Improvement: A security program that evolves with threats, regulations, and your business growth. Security is a journey, not a destination.
Clients typically see measurable security posture improvement within the first 90 days of engagement
vCISO Investment and Engagement Options
Security leadership shouldn't require a full-time executive salary. Our vCISO engagements are structured to deliver enterprise-grade security guidance scaled to your organization's size and needs.
We offer flexible engagement models—from strategic advisory for organizations with internal IT capabilities to comprehensive program management for regulated industries. Most mid-sized organizations invest significantly less than a full-time CISO while gaining access to experienced security leadership.
Learn more about our engagement models and get a customized quote on our vCISO Pricing page.
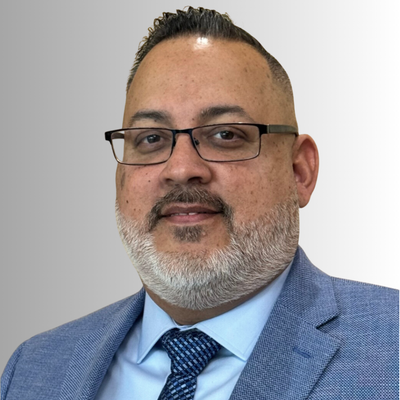
Meet Your Security Leadership
"We don't just secure your network. We sit on your side of the table during board meetings."
Dan Pitre
Founder & Senior vCISO
Enterprise security leadership serving regulated industries. Leading a team of security professionals who bring board-level strategy to organizations without the full-time executive cost.
Business outcomes with vCISO & Governance
Virtual CISO services, governance frameworks, risk assessments, and insurance-aligned cybersecurity leadership for growing organizations.
Key Results
- Create an executive-owned cyber risk program
- Align cybersecurity with business and board priorities
- Standardize policies, procedures, and controls
- Strengthen insurance readiness and renewal conversations
Challenges We Solve
We understand the unique hurdles different industries face when securing their digital infrastructure.
Creative Agencies
- Client asset theft and IP exposure
- Unsecured contractor access
- Weak email authentication impacting deliverability
- File-sharing risks between clients and creatives
Financial Services
- Increasing regulatory pressure from SEC, FINRA, CFPB, and state agencies
- Rising cyber insurance requirements and premium hikes
- Email-based fraud targeting advisors, lenders, and back-office staff
- Client data exposure risks across cloud apps, devices, and remote users
Nonprofits
- Protect donor data
- Reduce accidental data exposure
- Modernize outdated systems
Healthcare
- PHI exposure risk
- Ransomware targeting medical practices
- Complex device & endpoint environments
- HIPAA compliance gaps
Professional Services
- Client confidentiality exposure
- Increasing insurance carrier requirements
- Unsecured file sharing with clients
- Remote/hybrid device security gaps
Construction / Trades
- Subcontractor access risks
- Ransomware targeting project files and drawings
- Distributed crews accessing data from the field
- Insurance and bonding requirements increasing
Comprehensive Services
Cyber Insurance Readiness
Prepare your business to meet cyber insurance requirements.
Cyber Risk Assessment
Identify and prioritize your organization's cybersecurity risks.
Virtual CISO (vCISO)
Expert security leadership without the cost of a full-time executive.
What Does vCISO Cost for Your Organization?
Every organization is different. Our quick assessment helps you understand which engagement model fits your needs and provides budgetary guidance—no sales call required.
- Tailored to your industry and size
- Compare engagement models side-by-side
- Receive personalized recommendation
Services
Cyber Insurance Alignment
Insurers look for strong governance. We provide the policies, incident response planning, and board-level reporting that demonstrate security maturity. Our vCISO engagements ensure you have documented evidence of security leadership that underwriters require during renewals.
Alignment with underwriting requirements helps reduce premiums and ensures claim validity.
Verified Controls
Incident Response Plan
Required for claims and reduces breach impact.
Logging & Monitoring
Insurers require logs for forensic evidence and claims approval.
Risk Assessment
Used by insurers to assess risk maturity before issuing policies.
Encryption
Reduces breach severity and limits reportable incidents.
Backups
Required by insurers to reduce claim cost and prevent total data loss.
Multi-Factor Authentication (MFA)
Stops the most common cause of claims: unauthorized access via password-only credentials.
Explore our other services
vCISO & Governance works best alongside our other core capabilities.
Industries we serve with vCISO & Governance
vCISO & Governance services by location
We provide vCISO & Governance services to organizations across the United States.
Frequently Asked Questions
Dan Pitre
President & Principal Consultant
Over 25 years of experience in cybersecurity and IT leadership. Specializes in vCISO advisory and security governance for CPA firms, healthcare organizations, and SMBs navigating regulatory and insurance requirements.
Leadership Insights
Hear from industry leaders on building security-conscious organizations where cybersecurity is everyone's responsibility.
We're Not Protecting Data—We're Protecting People
Bob Shannon, CEO of Assured Performance 360 and founder of the Las Vegas Fire/Rescue Leadership Academy, discusses why cybersecurity is fundamentally about protecting people and how leadership principles from emergency management apply to building security-conscious organizations.
Watch all episodesNot Sure If a vCISO Is the Right Fit?
Compare the virtual CISO and full-time CISO models side by side — cost, availability, compliance expertise, and when each makes sense for your organization.
vCISO vs. Full-Time CISO — Complete Comparison GuidevCISO Pricing: What Does It Cost?
Typically 60-80% less than a full-time CISO. Pricing depends on organization size, compliance needs, and engagement depth.
See detailed pricing & get your custom quoteLatest Compliance Intelligence
HIPAA 2026: Major Security Rule Changes Ahead
The HIPAA Security Rule is getting its biggest overhaul in decades. See how these 2026 changes affect your compliance strategy.
HIPAA 2026 Security Rule ChangesWhen AI Accelerates the Patch-Window Race
Some frontier models have now demonstrated autonomous vulnerability discovery, compressing the window between disclosure and exploit. A governance-first playbook for security leaders whose patch cycles must now assume a faster adversary.
Read the PlaybookCMMC Phase 2: Are You Ready for November 2026?
Phase 1 is already enforcing. Phase 2 requires C3PAO third-party certification for defense contractors handling CUI. Learn the timeline and what to do now.
CMMC Phase 2 Deadline — What Defense Contractors Need to KnowCMMC Level 1: The Complete Self-Assessment Guide
15 controls, 59 assessment objectives, zero room for POA&Ms. A practitioner's walkthrough of every requirement for defense contractors pursuing Level 1 compliance.
CMMC Level 1 Self-Assessment — The Complete Practitioner's GuideTelehealth HIPAA Compliance After Enforcement Discretion
OCR's enforcement discretion for telehealth expired on May 11, 2023, with the 90-day transition period ending August 9, 2023. Providers operating mixed workflows across video, audio, and messaging now face the full scope of HIPAA obligations — from BAA gap analysis to tracking-technology compliance.
Read the Telehealth Compliance GuideHealthcare Organizations
HIPAA-regulated? Our healthcare vCISO program is built specifically for covered entities and business associates — from risk assessment to OCR audit readiness.
Healthcare vCISO Services